
Security Engineer / DevOps Engineer
Firewall-as-Code - Automated Policy Cleanup
The Business Problem
After a project completes, stale security groups and rules need cleanup. Manually writing API scripts requires deep knowledge of the NSX Manager API (hundreds of methods), careful dependency ordering, robust error handling, and thorough testing. Typical timeline: 1-2 weeks for a complex cleanup operation.
Writing this script incorrectly - wrong deletion order, missing dependencies, inadequate error handling - risks breaking production firewall policy mid-execution.
How Zenera Solves It
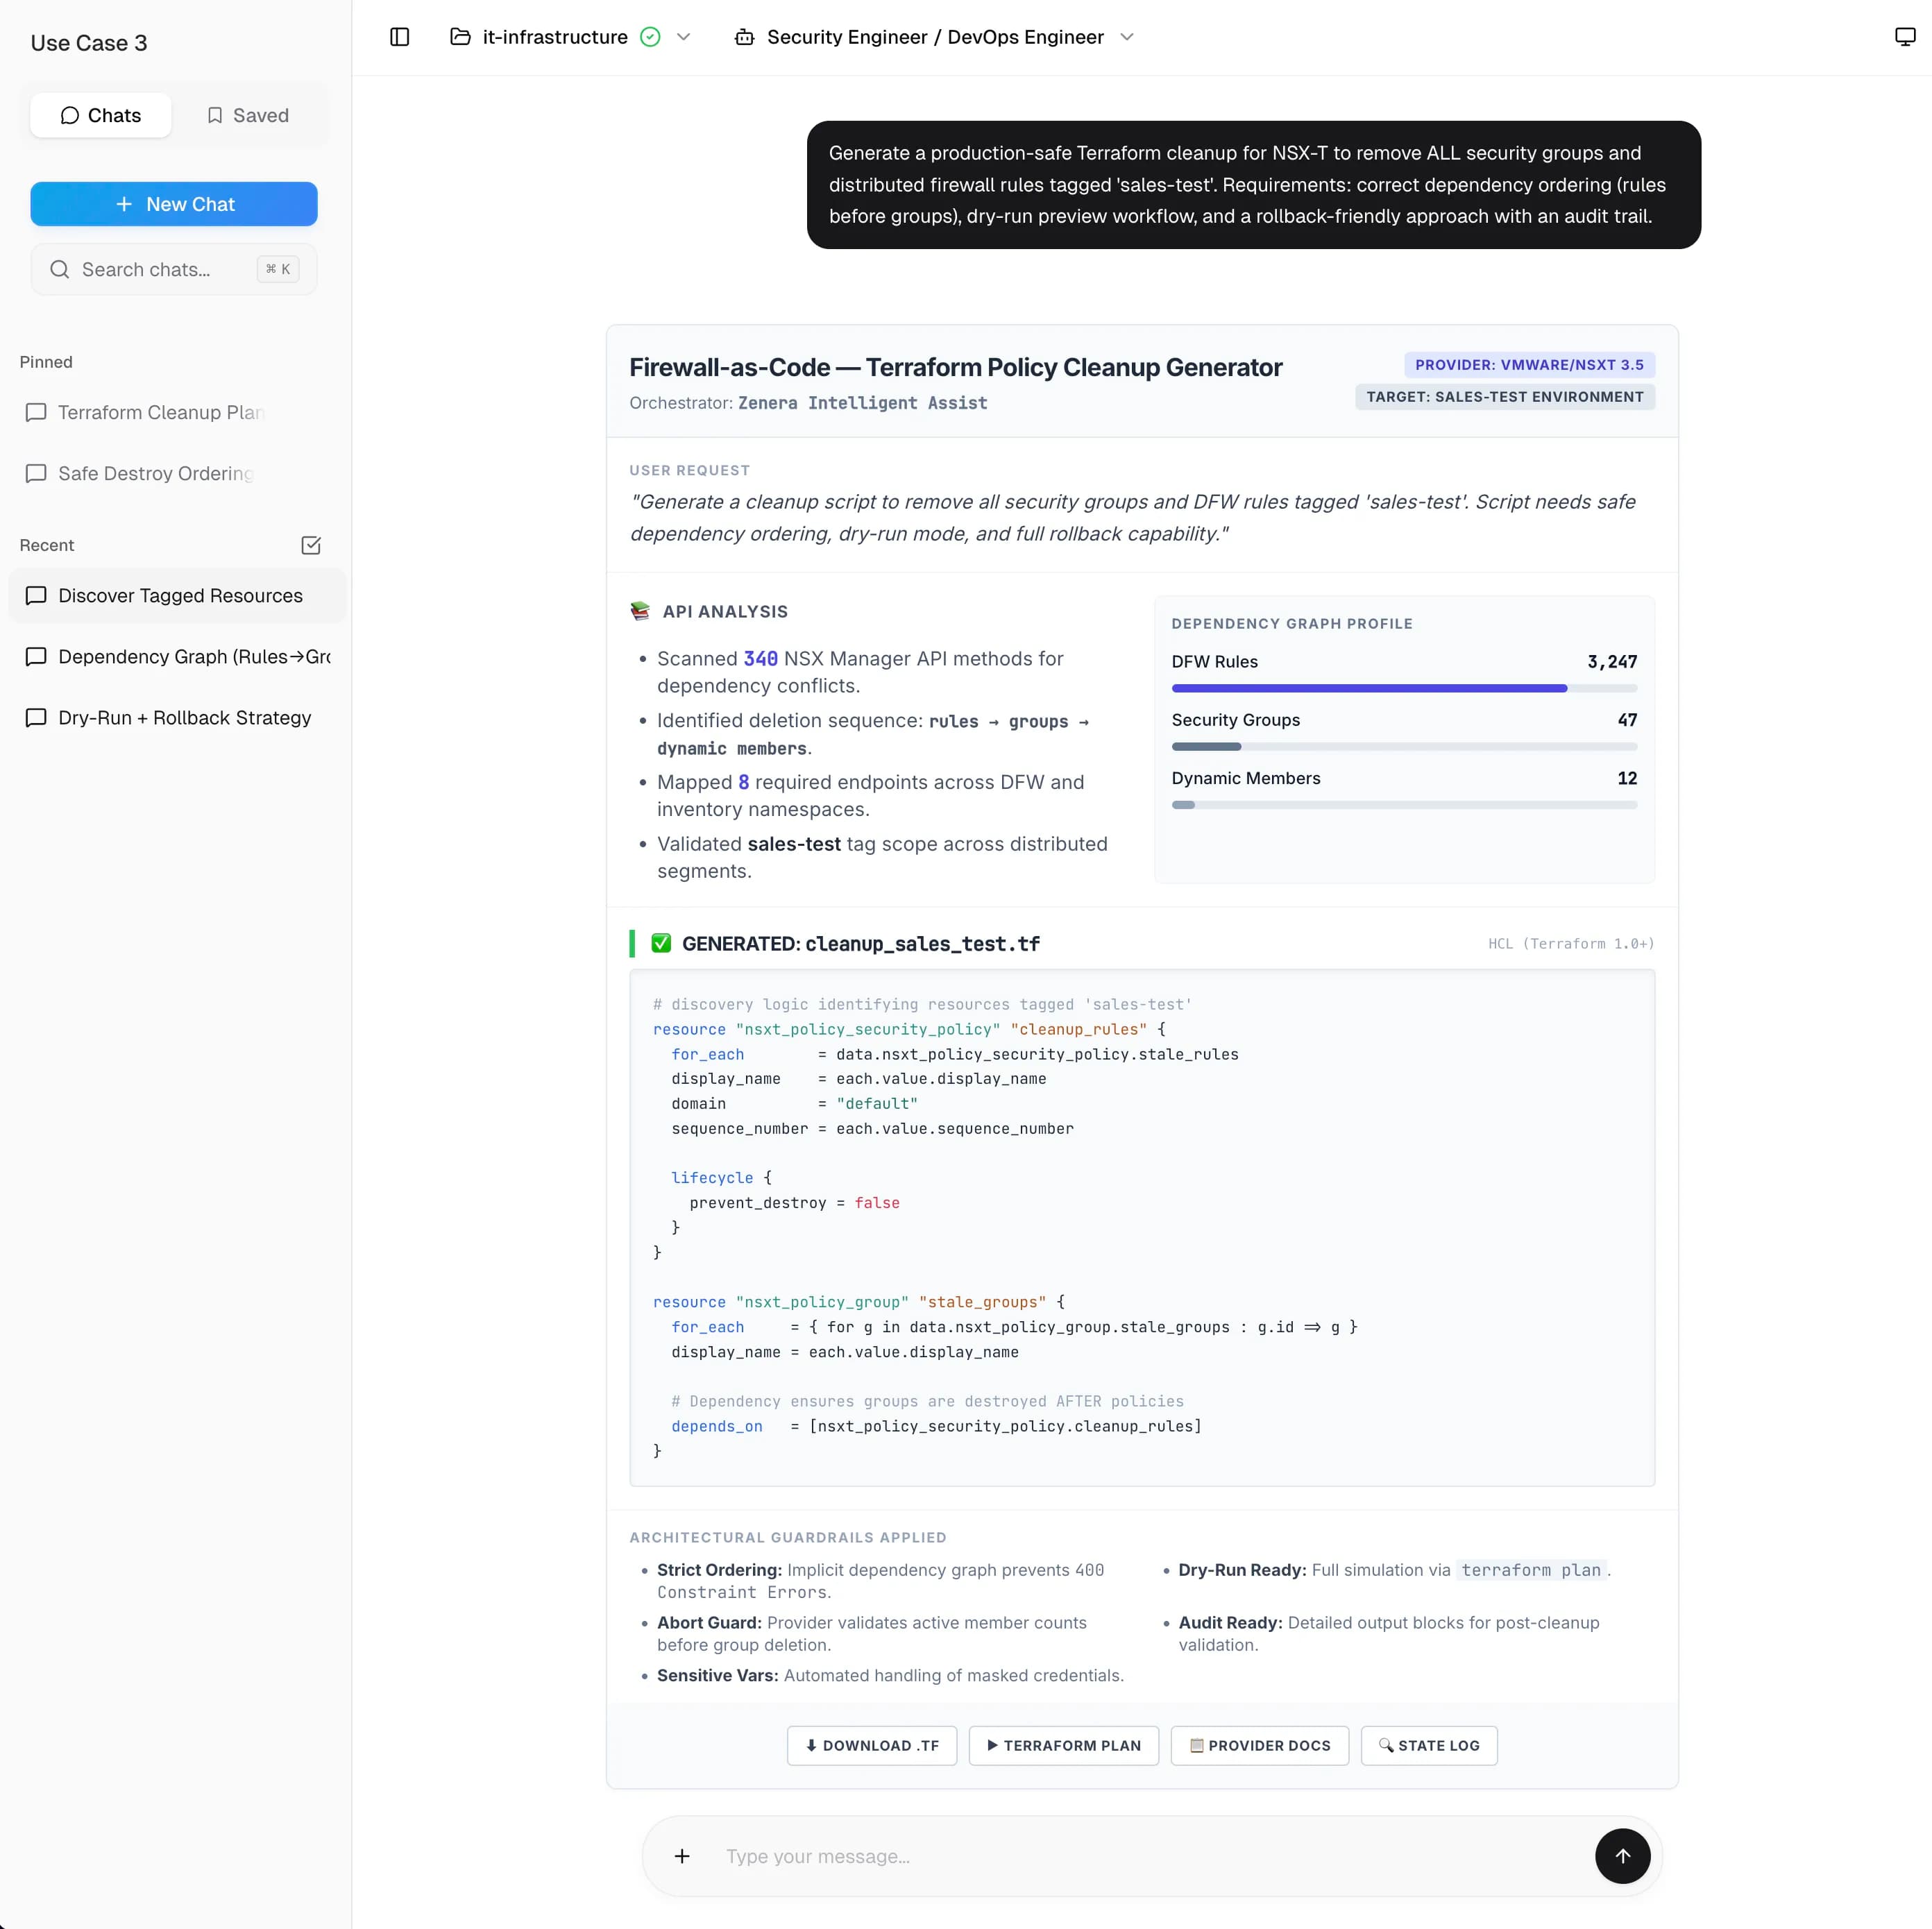
Intelligent Assist execution:
- 1Natural language parsing: Understood the cleanup request including the requirements for safe dependency ordering, dry-run preview, and rollback capability - mapping each to native Terraform idioms (terraform plan, depends_on, terraform destroy)
- 2Provider schema comprehension: Scanned the vmware/nsxt 3.5 provider resource catalog to identify nsxt_policy_security_policy and nsxt_policy_group as the correct resource types, including their membership-validation behavior on destruction
- 3Dependency ordering: Encoded rules-before-groups destruction order via explicit depends_on, leveraging Terraform's declarative graph to guarantee correct sequencing without manual orchestration
- 4Best-practice generation: Marked credentials sensitive, added prevent_destroy = false with a documented override path for manual approval gates, and included output blocks that produce an audit trail of every resource targeted
Time to production-ready Terraform
2 minutes (vs. 1-2 weeks of manual development and testing)